CISA certification: requirements, exam format and practice questions
CISA (Certified Information Systems Auditor) is a certification from ISACA. The exam is 150 questions across five job practice domains, and certification additionally requires five or more years of professional information systems auditing, control or security experience.
- Questions
- 150, across five job practice domainsISACA exam content outline, checked 10 October 2026
- Domain weightings
- 18% auditing process, 18% governance, 12% acquisition and development, 26% operations and resilience, 26% protection of assetsISACA exam content outline, checked 10 October 2026
- Experience required
- Five or more years in IS auditing, control or securityISACA, Earn a CISA certification, checked 24 September 2026
- Exam validity for applying
- The exam must have been passed within the last five yearsISACA, Earn a CISA certification, checked 24 September 2026
- Application fee
- US$50, one-timeISACA states a one-time US$50 application processing fee, checked 24 September 2026
- CPE to keep it
- 20 CPE hours a year, 120 over three yearsISACA, Maintain CISA certification, checked 24 September 2026
- Annual maintenance fee
- $45 for members, $85 for non-membersISACA, Maintain CISA certification, checked 24 September 2026
- Exam fee
- US$575 for ISACA members, US$760 for non-membersISACA CISA page and exam candidate guide v1.26, checked 10 October 2026
- Exam duration
- 4 hours (240 minutes)ISACA exam candidate guide v1.26, checked 10 October 2026
- Passing score
- 450 on a scale of 200 to 800ISACA exam candidate guide v1.26, checked 10 October 2026
- Practice questions here
- 500 for the CISA examCertsqill question bank
Know if you're ready for CISA — before you book.
Certsqill measures your CISA readiness across every official exam domain — one 0–100 score from coverage, accuracy and consistency that tells you whether to book, keep studying, or sit.
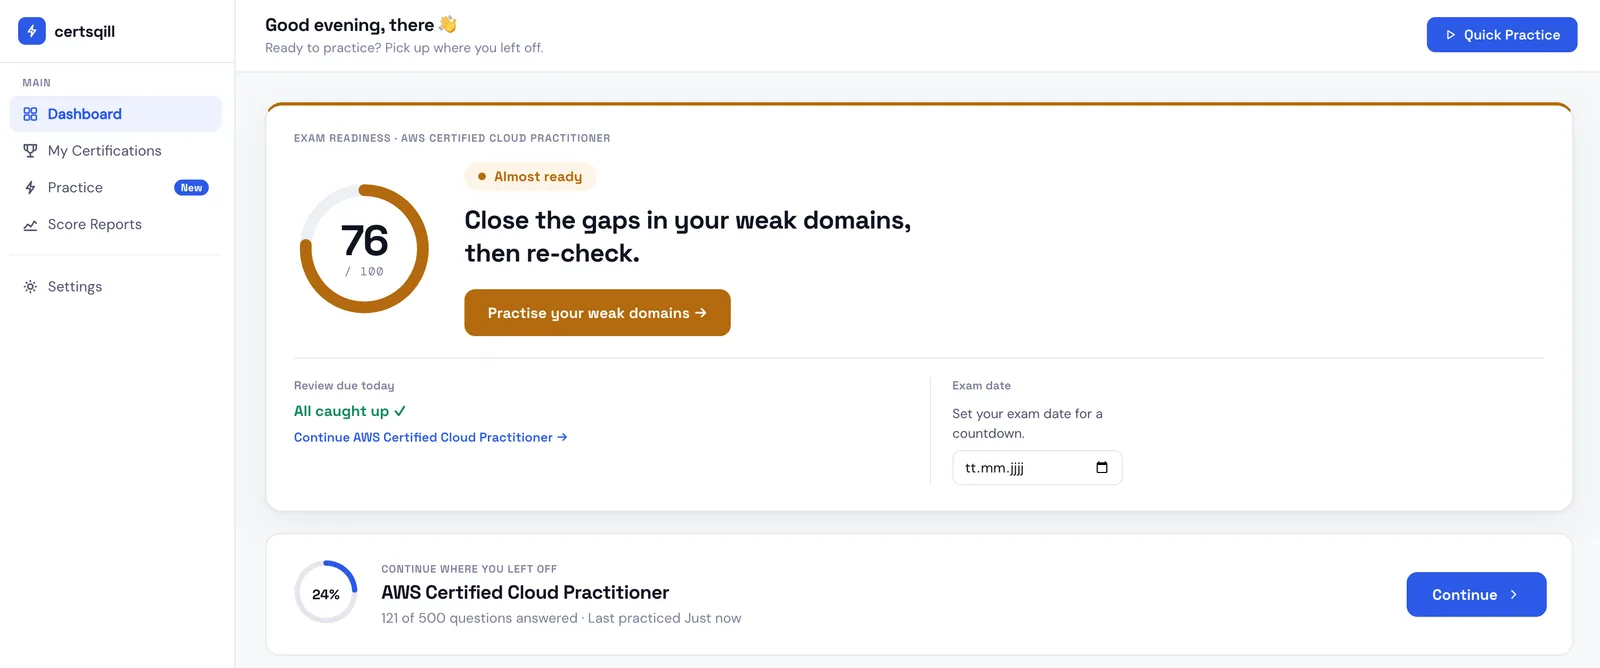
See exactly how you'll know you're ready.
Answer one question. See exactly how Certsqill measures your CISA readiness.
A live demo of the product loop: a practice question is answered incorrectly, the AI tutor explains why, the weak domain updates, and the readiness score moves toward the exam-ready threshold of 80. Figures shown are a representative demo.
Why people switch to Certsqill
Everything you need to walk in ready
Know where you stand, understand every mistake, and study in your language — one payment, no subscription.
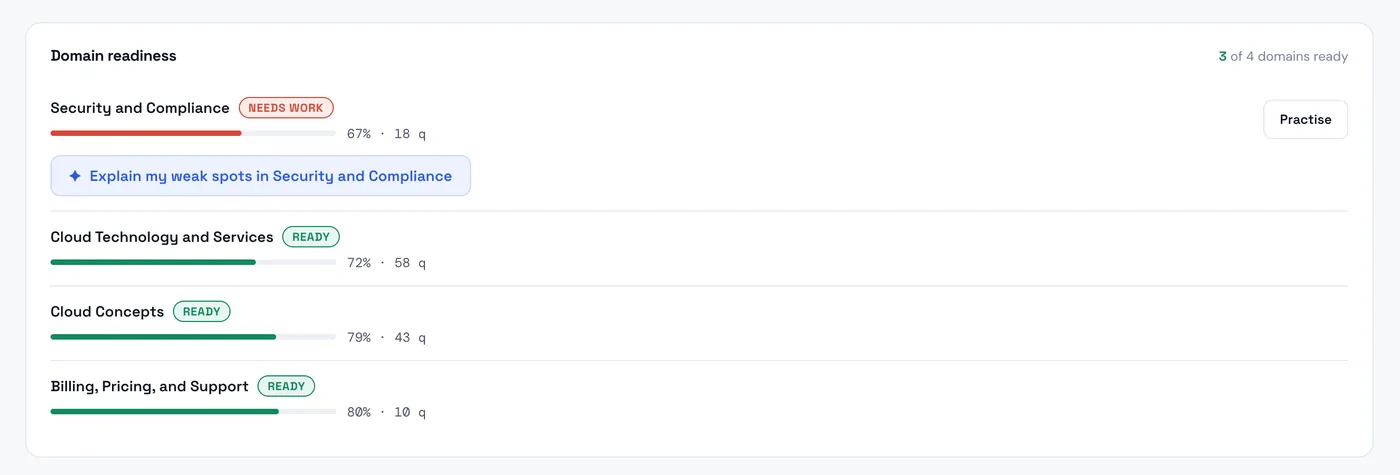
Your CISA Readiness Score, not a guess
One number from three signals — coverage, accuracy, and consistency — tells you whether to book the exam or keep studying.
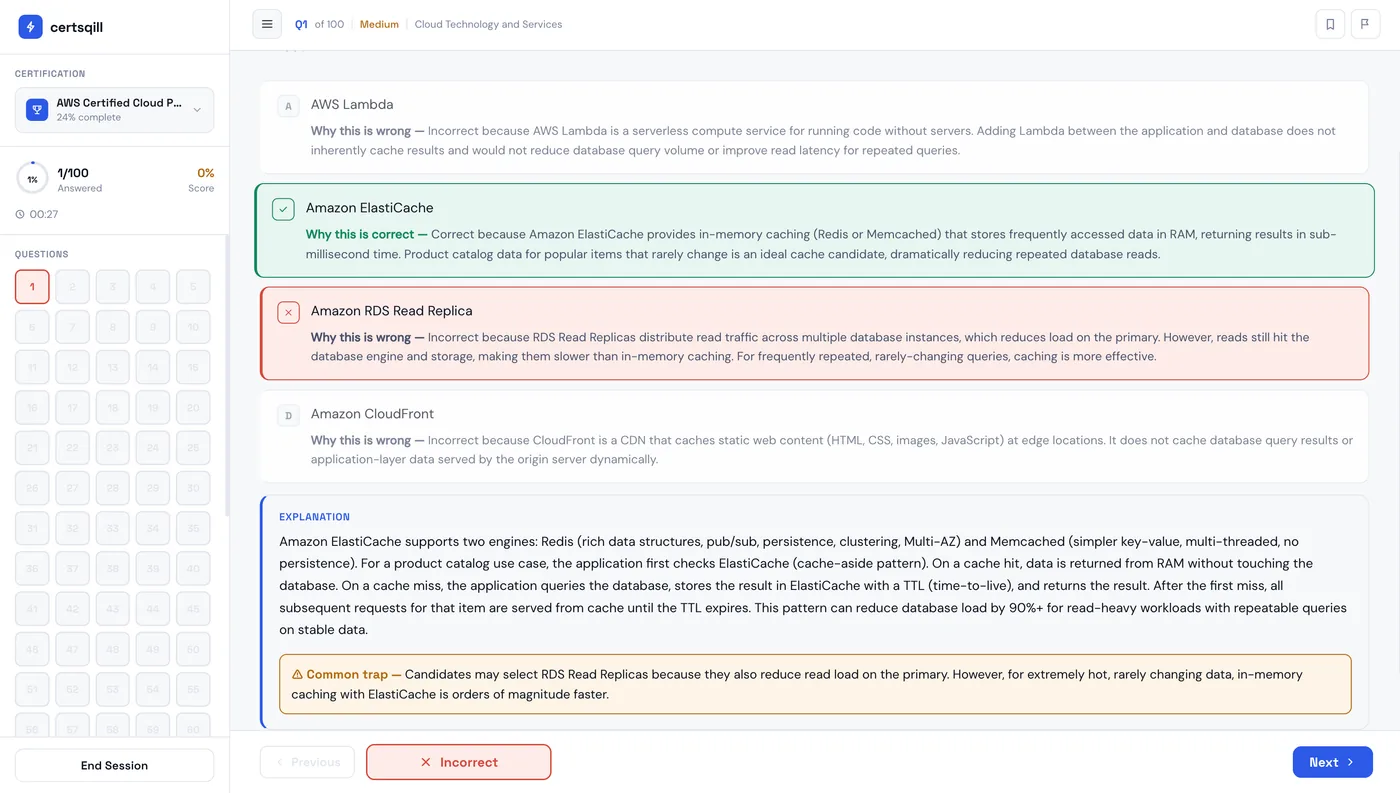
Understand every CISA mistake
When you miss a question, it explains why — using your own answer history to catch the patterns you keep repeating. Included, no subscription.
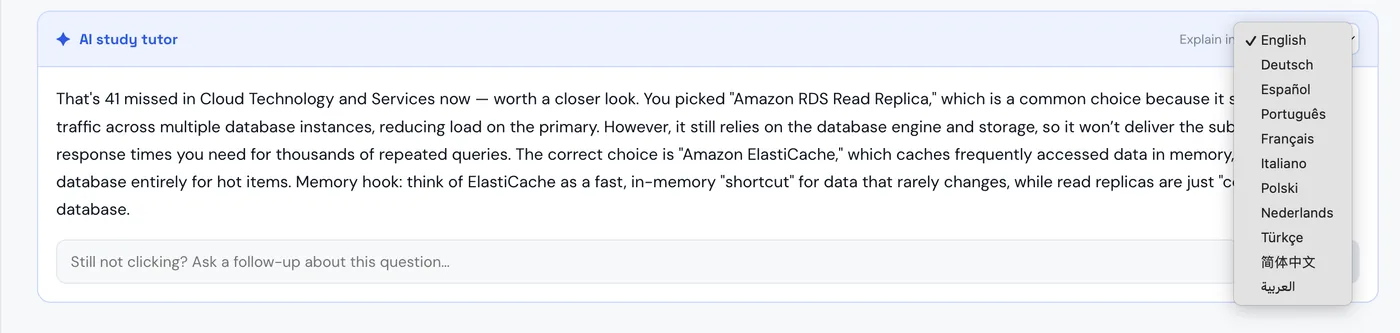
Explanations in your language, questions stay exam-accurate
Get every explanation in your language while the questions stay in exam-accurate English. Technical terms stay in English — the way the exam writes them.
Everything you need to pass
Why you can trust these CISA questions
What is a CISA?
CISA stands for Certified Information Systems Auditor, a certification from ISACA. It is the auditor’s credential, not the defender’s, and narrower than most security credentials: it shows that you can audit information systems — the controls, the governance, the resilience — rather than build or defend them. In cyber security terms, it is the audit seat.
One thing to clear up first, because it splits the search results: there are two CISAs. This page is about the ISACA certification. The other CISA is the US Cybersecurity and Infrastructure Security Agency, the government body behind the KEV catalogue and the incident response playbooks. Different thing entirely.
ISACA states that more than 200,000 people have obtained the certification since 1978.
Source: ISACA — CISA certification. Checked 24 September 2026.
What is the CISA exam?
The CISA exam consists of 150 questions covering five job practice domains. That is the CISA exam format as ISACA publishes it — 150 questions, five domains, one sitting. The domains and their weights are:
- Information Systems Auditing Process — 18%
- Governance and Management of IT — 18%
- Information Systems Acquisition, Development and Implementation — 12%
- Information Systems Operations and Business Resilience — 26%
- Protection of Information Assets — 26%
Source: ISACA — CISA exam content outline. Checked 10 October 2026.
What are the CISA requirements?
The CISA requirements are two, and the exam is only one of them. ISACA requires that you pass the CISA exam within the last five years, and that you have five or more years of professional information systems auditing, control or security work experience.
So the exam requirements and the certification requirements are not the same thing. There are no prerequisites for sitting the exam — you can book it whenever you like. The work experience requirement is what the application checks afterwards, once your scores are released.
There is also a one-time US$50 application processing fee.
Source: ISACA — Earn a CISA certification. Checked 24 September 2026.
How much does the CISA exam cost?
The CISA exam fee is US$575 for ISACA members and US$760 for non-members. ISACA shows both figures on its CISA page, and its candidate guide states that the fee is based on membership status at the time of exam registration.
The same candidate guide, version 1.26, gives the exam duration and the passing score: 4 hours (240 minutes) for 150 multiple-choice questions, scored on a scale from 200 to 800, with 450 or higher needed to pass. Checked on 10 October 2026.
On top of the exam fee comes the US$50 application processing fee, which is separate from the exam. So a page quoting you a single CISA cost is leaving something out: the exam fee depends on your membership status, and the application fee follows once you pass.
Source: ISACA — Certification Exam Candidate Guide (CISA, CISM, CGEIT, CRISC, CDPSE), version 1.26. Checked 10 October 2026.
What are the CISA CPE requirements?
Keeping the certification is its own obligation. ISACA requires a minimum of 20 CPE hours annually and a total of 120 CPE hours over a three-year reporting period.
On top of the hours there is an annual maintenance fee: $45 for ISACA members, $85 for non-members. ISACA states that failure to comply with these requirements results in revocation of the designation.
Source: ISACA — Maintain CISA certification. Checked 24 September 2026.
How hard is the CISA exam?
Nobody outside ISACA can put a number on how hard the CISA exam is, because ISACA publishes no pass rate. It does publish the passing score — 450 on a scale of 200 to 800 — but that is a score on ISACA’s scale, not a percentage. Anyone quoting you a CISA failure rate is quoting a survey, not the issuer.
How hard CISA is against its neighbours is a fairer question. The usual comparison is with CISSP, and the two are hard in different directions: CISSP tests the breadth of security design, CISA tests audit judgement — whether a control is adequate, evidenced and independent.
There is no official answer to how long to study for CISA either. ISACA sets no study-hours figure. What it does set is 150 questions over five domains and a five-year experience requirement, which means most candidates are already doing the work the exam asks about.
Source: ISACA — Certification Exam Candidate Guide (CISA, CISM, CGEIT, CRISC, CDPSE), version 1.26. Checked 10 October 2026.
Where can you find CISA practice questions?
This site holds 500 CISA practice questions across the five domains. Every question shows all options, which one is correct, and why each of the others is wrong — on an audit exam, the wrong answers are usually the ones that would be right in a different control environment.
The point of practice questions is to meet ISACA’s phrasing before exam day.
What you will not find here are CISA exam dumps built from recycled live exam content. These questions are written against ISACA’s published exam content outline instead — the part that stays true when ISACA rotates its item bank.
Because ISACA’s pass mark is 450 on a scale of 200 to 800 rather than a percentage, no practice percentage can tell you that you have passed. What it can tell you is which of the five domains still costs you points.
What CISA study material do you need?
ISACA sells its own: a review manual, an online course, and the CISA Questions, Answers & Explanations database.
They all point back at the same five domains in the exam content outline. This site is not a course and does not resell ISACA material; it is the practice layer on top of whichever manual you use.
Source: ISACA — CISA certification. Checked 24 September 2026.
CISA vs CISM, CISSP, CRISC and CPA
CISA vs CISM stays inside ISACA: CISA audits systems, CISM manages security. CISA vs CRISC is audit against risk. CISSP vs CISM vs CISA is the three-way version of the same question — design, manage, audit — and CISA vs CISSP crosses issuers, ISC2’s CISSP being the broad security design certification and ISACA’s CISA the audit one.
CISA vs CPA crosses professions entirely: the CPA is an accounting licence issued by US state boards, CISA an information systems audit certification issued by ISACA. CIA vs CISA is closer — the Certified Internal Auditor covers internal audit generally, CISA the information systems part of it. None of these replaces another.
Source: ISACA — CISA certification. Checked 24 September 2026.
Is CISA certification worth it?
ISACA’s CISA overview displays “US$149K+ average annual salary” and “22% received a pay boost”, without naming the survey, the year or the countries behind either figure (checked 10 October 2026). Treat them as ISACA’s headline numbers, not as a benchmark for a particular market or role.
What can be stated is the price of entry: 150 questions across five domains, an exam fee of US$575 for members or US$760 for non-members, five or more years of documented IS audit experience, a one-time US$50 application fee, then 20 CPE hours a year and an annual maintenance fee of $45 for members or $85 for non-members. Whether that is worth it depends on whether audit is the chair you want to sit in.
Source: ISACA — Maintain CISA certification. Checked 24 September 2026.
CISA questions people ask
What is a CISA?
CISA is the Certified Information Systems Auditor certification from ISACA. The exam is 150 questions across five domains, and certification requires five or more years of IS auditing, control or security experience. Source: ISACA, checked 24 September 2026. Note that the US Cybersecurity and Infrastructure Security Agency uses the same abbreviation; this is the certification.
What does CISA stand for?
CISA stands for Certified Information Systems Auditor. Source: ISACA CISA certification page, checked 24 September 2026.
What are the CISA certification requirements?
Pass the CISA exam within the last five years, and have five or more years of professional information systems auditing, control or security work experience. A one-time US$50 application processing fee applies. Source: ISACA, checked 24 September 2026.
How many questions are on the CISA exam?
150, covering five job practice domains weighted 18%, 18%, 12%, 26% and 26%. Source: ISACA exam content outline, checked 10 October 2026.
What is the CISA pass score?
450 or higher, on ISACA’s scale of 200 to 800. Source: ISACA exam candidate guide v1.26, checked 10 October 2026.
What are the CISA certification fees?
The exam fee is US$575 for ISACA members and US$760 for non-members. On top come a one-time US$50 application processing fee and an annual maintenance fee of $45 for members and $85 for non-members. Source: ISACA CISA page and exam candidate guide v1.26, checked 10 October 2026.
What are the CISA CPE requirements?
A minimum of 20 CPE hours annually and 120 CPE hours over a three-year reporting period, plus the annual maintenance fee. ISACA states that failure to comply results in revocation. Source: ISACA, Maintain CISA certification, checked 24 September 2026.
Is CISA certification worth it?
ISACA’s CISA page shows “US$149K+ average annual salary” without naming the survey or year behind it, so it is a headline figure, not a benchmark. What ISACA also publishes: 150 questions across five domains, an exam fee of US$575 for members or US$760 for non-members, five or more years of documented IS audit experience, a one-time US$50 application fee, 20 CPE hours a year and an annual maintenance fee of $45 for members or $85 for non-members. Checked 10 October 2026.
Is CISA the certification or the government agency?
Both use the abbreviation. This page is about ISACA’s Certified Information Systems Auditor. The US Cybersecurity and Infrastructure Security Agency is a separate organisation and is not covered here.
How many CISA practice questions does Certsqill have?
500 for the CISA exam, each with an explanation for every option — the correct one and the wrong ones.
What is the CISA certification worth to an employer?
What is the CISA certification in practical terms? It is an audit certification that combines a passed exam with experience someone else has vouched for. ISACA asks for five or more years of information systems auditing, control or security work, gained within the 10 years before you apply, and that experience has to be verified by a supervisor or manager.
That is what separates a CISA certified auditor from someone who has only passed the CISA certification exam. CISA holders also agree to ISACA’s Code of Professional Ethics and to adhere to the Information Systems Auditing Standards adopted by ISACA — which is why the credential carries weight in audit reports and engagement teams.
Source: ISACA — Earn a CISA certification. Checked 9 October 2026.
What is CISA exam day like?
The ISACA CISA test is computer-based: 150 multiple-choice questions in four hours, taken at a PSI testing centre or as a remotely proctored exam. Results are reported on a scale from 200 to 800, 450 is the pass mark, and you see a preliminary passing status on screen when you finish. The official score follows within 10 working days.
First you pass the CISA exam. Certification comes later: only after the official score is released can you apply, and you have five years from the passing date to do so.
Source: ISACA — Certification Exam Candidate Guide (CISA, CISM, CGEIT, CRISC, CDPSE), version 1.26. Checked 9 October 2026.
The CISA syllabus: domain weights
ISACA does not call it a syllabus, but the CISA exam content outline is exactly that: it lists every topic the CISA certification test can cover, grouped into five domains with published weights.
- Information Systems Auditing Process — 18%
- Governance and Management of IT — 18%
- Information Systems Acquisition, Development and Implementation — 12%
- Information Systems Operations and Business Resilience — 26%
- Protection of Information Assets — 26%
Source: ISACA — CISA exam content outline. Checked 9 October 2026.
Does CISA cover pen testing?
Not as a hands-on skill. The term penetration testing does not appear in ISACA’s CISA outline. What does appear, in the Protection of Information Assets domain, is “Security Testing Tools and Techniques” and “Information System Attack Methods and Techniques”, and one of the outline’s tasks is to use technical security testing to identify potential vulnerabilities.
So CISA pen testing knowledge is the auditor’s view: knowing what a test should cover, judging whether its scope and evidence are adequate, and assessing the findings. If you want a certification for carrying out CISA penetration testing work yourself, an audit credential is the wrong tool — CISA certifies the person who reviews the test, not the person who runs it.
Source: ISACA — CISA exam content outline. Checked 9 October 2026.
How to register for CISA exam seats
CISA exam registration is continuous: ISACA states that you can register at any time, with no restrictions. You register and pay through ISACA, and from that day you have a six-month eligibility period to take the exam.
After payment you are taken to the PSI dashboard to book an appointment. The earliest slot is 48 hours after payment, and appointments open only 90 days in advance. You do not need the five years of experience to register — the CISA isaca exam is open to anyone, and experience is checked when you apply for certification.
Source: ISACA — CISA certification. Checked 9 October 2026.
CISA certification jobs
CISA certified jobs are the roles the experience requirement describes: information systems auditing, control and security. In practice that means IT audit, internal audit with a technology focus, IT risk and compliance, and security assurance work where you assess controls rather than build them. ISACA also runs a career centre with job listings for its community.
Because the experience must be verified by a supervisor or manager, jobs with CISA certification as a requirement can rely on it as evidence of practice, not only of exam knowledge. It also means jobs for CISA certified professionals sit above entry level by design: the credential itself requires five years of relevant experience.
Source: ISACA — Earn a CISA certification. Checked 9 October 2026.
CISA jobs, salary and what ISACA states
For CISA salary figures, ISACA’s overview displays “US$149K+ average annual salary” and lists “22% received a pay boost” among the benefits. The page does not name the survey, the year or the countries behind either figure, so treat them as ISACA’s headline numbers rather than a benchmark for a particular market or role.
Source: ISACA — CISA certification. Checked 9 October 2026.
How to renew CISA each year
CISA is not a one-time achievement. To renew it, you report at least 20 CPE hours every year and 120 over each three-year period, and pay the annual maintenance fee — $45 for ISACA members, $85 for non-members. ISACA states that failing to meet these requirements results in revocation.
Whether you prepare with a boot camp, a bootcamp-style weekend or self-study, the same renewal cycle starts once you are certified, so it is worth keeping a record of CPE-eligible training from the beginning.
Source: ISACA — Maintain CISA certification. Checked 24 September 2026.
More CISA questions
What does CISA certification stand for?
Certified Information Systems Auditor. Holders agree to ISACA’s Code of Professional Ethics and its Information Systems Auditing Standards. Source: ISACA, checked 9 October 2026.
Is the CISA an audit certification or a security certification?
An audit certification. The experience it requires can come from IS auditing, control or security work, but the exam tests audit judgement across five domains. Source: ISACA, checked 9 October 2026.
Can I register for the CISA exam before I have five years of experience?
Yes. ISACA states that you can take the exam before meeting the experience requirement; you must meet it before certification, and you have five years from passing to apply. Checked 9 October 2026.
What does the CISA exam certification process look like?
Pass the exam, wait for the official score, pay the one-time US$50 application fee, and submit an application with experience verified by a supervisor or manager. Source: ISACA, checked 9 October 2026.
CISA in detail
Exam fee: $760 ($575 for members) — what the CISA exam costs, retakes included →

